Conditional Invocation Abuse
Attackers exploit conditional logic in agents to trigger sensitive tools under manipulated contexts.
2026 State of Agentic AI Security
How ready is your organization to secure AI agents?
3 quick questions. See how you compare to other security leaders.
Definition
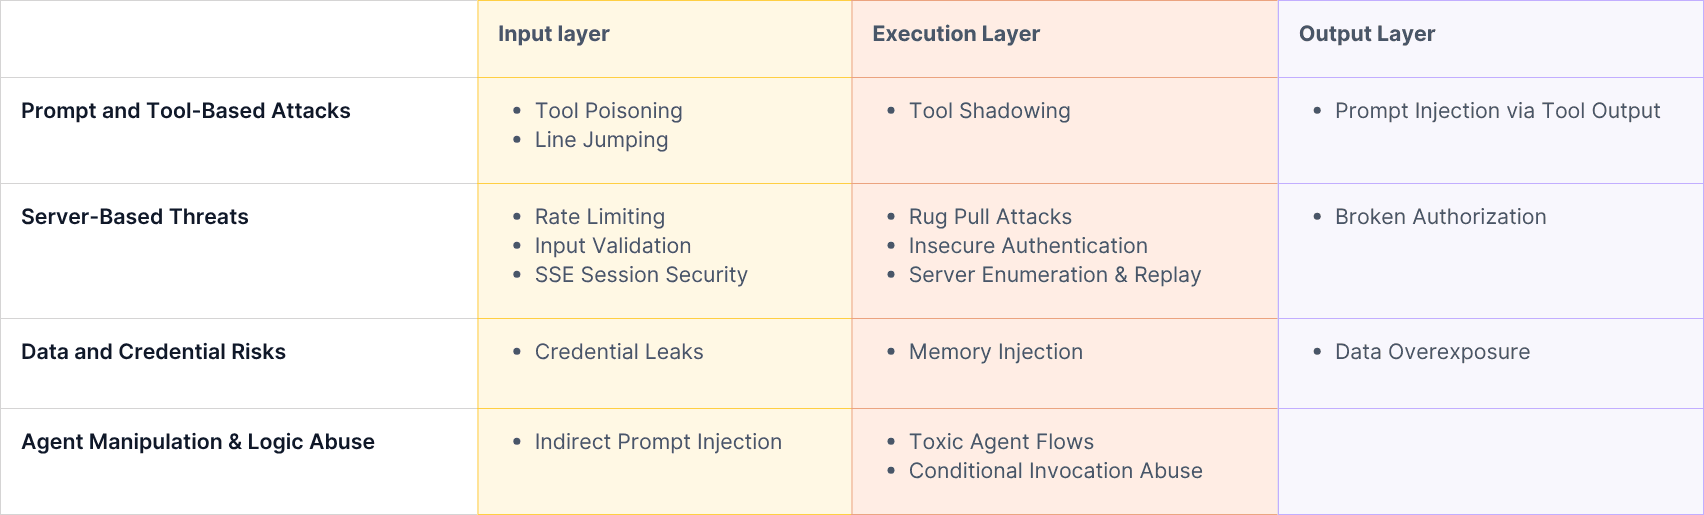
Conditional Invocation Abuse is an attack on the execution layer of the Model Context Protocol (MCP). It occurs when agents rely on loosely defined conditions to determine whether or not to invoke certain tools. Attackers craft inputs or manipulate context to satisfy these conditions and trigger tools that should remain inaccessible. This often happens in multi-step workflows where state, memory, or prompt content is used to determine tool execution.
This attack lives in the execution layer of the MCP model, where conditional logic governs when and how tools are invoked.
How MCP Security Helps
Akto identifies risky invocation patterns by simulating malicious condition triggers across agent flows. It analyzes tool call logic, detects bypasses in guard conditions, and runs contextual tests to ensure tools only execute under strict and verified scenarios.