Rate Limiting
Attackers rapidly trigger tool invocations, overwhelming infrastructure or bypassing usage controls.
2026 State of Agentic AI Security
How ready is your organization to secure AI agents?
3 quick questions. See how you compare to other security leaders.
Definition
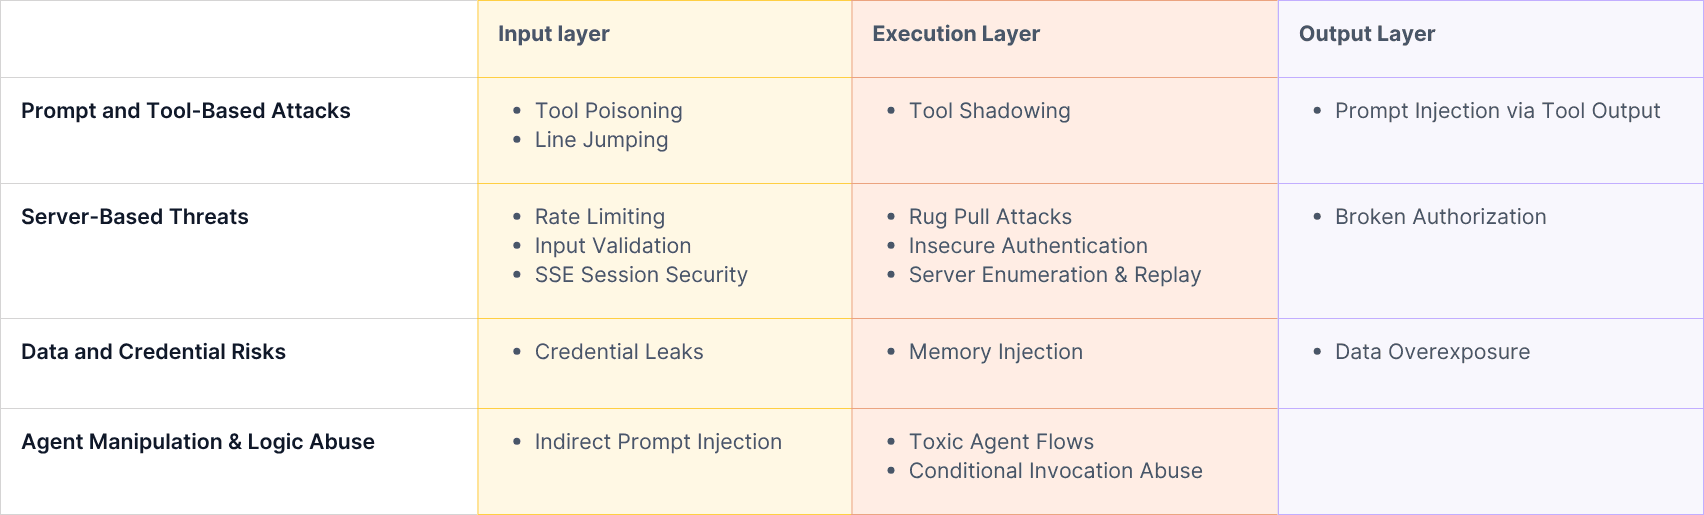
Rate Limiting attacks target the input layer of the Model Context Protocol (MCP). These attacks exploit the lack of invocation limits on MCP-compatible tools or APIs, allowing agents or adversaries to repeatedly call tools at high frequency. Without rate limits, this behavior can lead to infrastructure overload, quota exhaustion, or denial of service. In some cases, attackers can abuse tool calls to extract large volumes of data through repeated access.
This attack lives in the input layer of the MCP model, where external input drives excessive tool interaction before execution safeguards can activate.
How MCP Security Helps
Akto detects rate abuse by monitoring tool call frequency and usage patterns. It simulates rapid invocation bursts during testing, flags tools that lack throttle mechanisms, and alerts when agents exceed safe tool interaction thresholds based on session or identity context.