

82%
of analyzed MCP server implementations are vulnerable to path traversal attacks.
24K+
unique secrets exposed directly in MCP configurations across public GitHub repositories.
8.5%
of servers in the official MCP registry use OAuth with the rest relying on static API keys or no authentication.
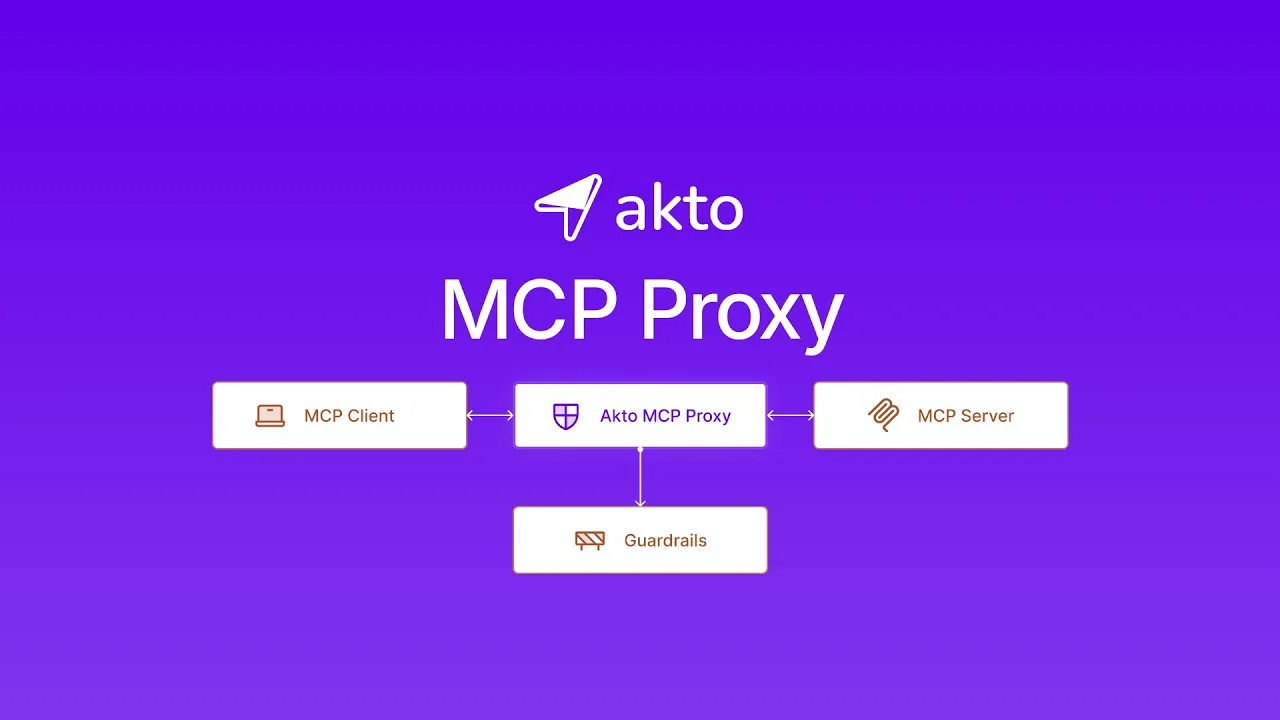
What Akto checks in an MCP interaction
Before execution
Akto evaluates the routed request against configured policies for risks such as prompt injection, credential exposure and unsafe tool use.
Policy decision
Requests that violate blocking policies are stopped before forwarding to the MCP server.
After execution
Akto checks the server response for sensitive data and other configured policy violations before returning it to the client.
Investigation
Request, response and guardrail records help security teams review the interaction and its outcome.
Authentication and credentials
Your existing MCP server authentication remains in place. The gateway forwards the authentication headers required by the upstream server; routing traffic through Akto does not itself replace those credentials with newly issued agent identities.
Coverage boundary
The gateway evaluates traffic routed through it. Direct connections and local actions that do not traverse the gateway require an appropriate additional enforcement path.
Connect, validate and expand MCP protection
No changes to existing MCP servers.
The gateway drops in front of your MCP servers without touching them. Keep your existing endpoints, tools, and credentials exactly as they are.
One config line per client to connect.
Point your MCP clients at a single Akto endpoint. One line of config per client, and traffic starts flowing through the gateway.
Configure, validate and expand
Obtain your organization’s gateway endpoint, update the MCP client configuration and validate the required policies on a test workflow. Expand coverage to additional clients and servers after confirming connectivity and enforcement.
MCP Security Cheatsheet
A practical guide to MCP architecture, top threats, and secure agentic AI
MCP Security Techniques
Advanced defense mechanisms for securing MCP server deployments at scale.

MCP Security: Buyer’s Toolkit and Checklist
This MCP Security Buyer's checklist outlines key requirements to evaluate MCP Security platforms across discovery, testing, runtime protection, integration, and governance.
Frequently asked questions
How is the MCP Gateway different from calling the Guardrails API?
What is Akto MCP Proxy?
How does the Akto MCP Gateway work?
Do I need to change my MCP servers to use it?
What threats does the Akto MCP Gateway stop?
What visibility do I get?